Endor Labs has launched AURI Fix for Open Source, a remediation engine that fixes open source vulnerabilities by editing application code rather than replacing or upgrading the vulnerable dependency itself. The company says internal research shows this approach can address the vast majority of reachable flaws far more often than traditional patching.
Why the usual patch-and-upgrade approach falls short
Endor Labs' research team examined 264,643 reachable vulnerabilities across codebases in financial services, insurance, cybersecurity and software companies. The team found that upgrading or patching the affected dependency resolved less than 10% of cases, often because newer versions break application functionality or no fix exists upstream. By contrast, 82% of the vulnerabilities could be neutralized with a small, targeted change to the application's own code, closing the exploitable path without touching the dependency at all.
The timing follows a tense week in open source security. On Oct. 21, PHP issued emergency patches for two critical vulnerabilities affecting an estimated 70% of websites. Exploitation attempts reportedly began within hours, prompting the EU's cybersecurity agency to warn that some sites might need to go offline, and officials in countries including Germany and Japan took government websites down temporarily while applying fixes.
How AURI Fix decides what to change
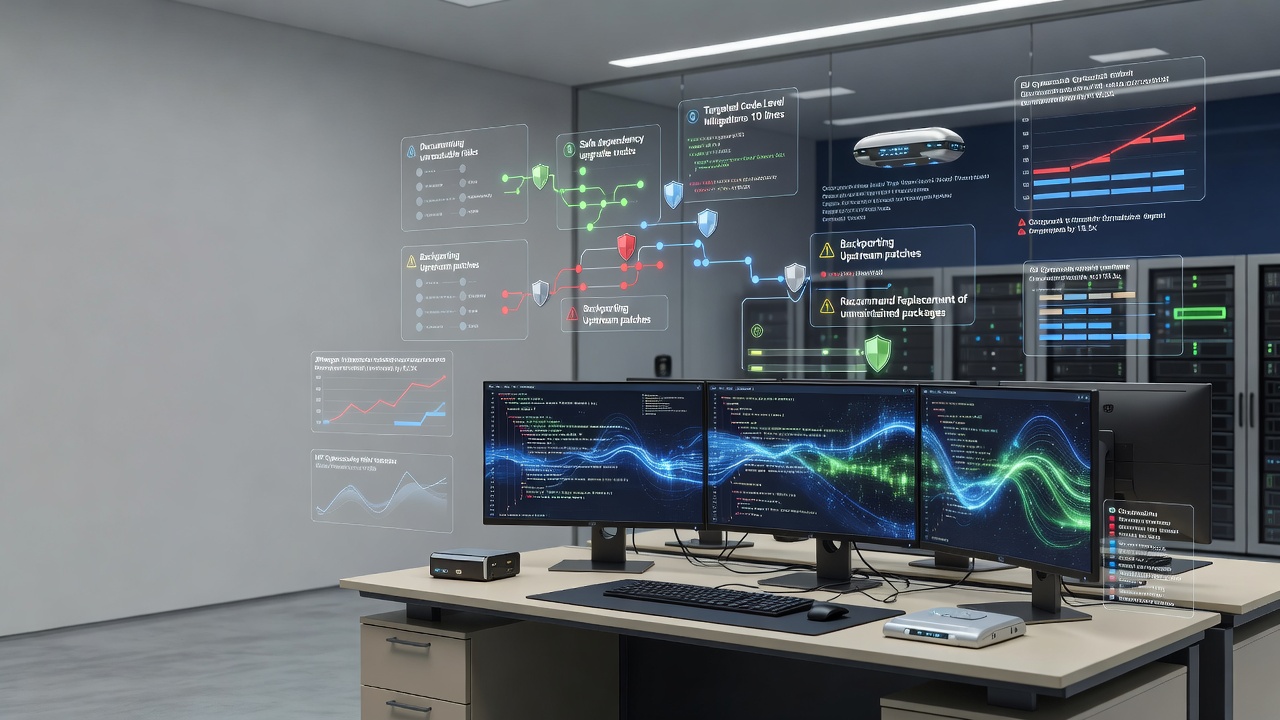
The tool evaluates each reachable vulnerability against a "code context graph" of the customer's application and selects from five remediation paths: documenting unreachable risk that needs no action, opening a pull request for a safe dependency upgrade, applying a targeted code-level mitigation (typically under 10 lines), backporting a patch when no upstream fix exists, or recommending replacement of an unmaintained or repeatedly vulnerable package. Teams can trigger fixes via the Endor Labs command-line tool or let an AURI agent triage findings and submit pull requests automatically for human review.
Each fix generates a VEX (Vulnerability Exploitability eXchange) report documenting why the vulnerability is no longer exploitable - evidence that downstream scanners, customers and auditors can use to suppress the finding, which the company notes is increasingly required under rules like the EU Cyber Resilience Act and FedRAMP.
Context: a widening gap between discovery and fixes
Endor Labs CEO Varun Badhwar said AI has sharply accelerated vulnerability discovery while remediation methods have lagged behind. The announcement cites a JPMorgan analysis finding that vulnerability discovery is outpacing remediation by a factor of 16.5, and notes the IMF recently flagged cybersecurity incidents at banks as a leading risk to global financial stability. These figures come from the organizations' own reporting as referenced by Endor Labs and have not been independently verified here.
Organizations considering automated code-level remediation should weigh how such changes are reviewed, tested and audited before deployment, since altering first-party code - even in small increments - still requires validation against existing application behavior and compliance requirements.